Avoid major mistakes that make your Android phone less secure and less convenient to use.
If you've used Android for a while, you probably know some of its most important rules. But even with an OS that's been around for more than 15 years, myths and outdated assumptions still persist. Or you might be new to Android and not totally sure how to best take care of your device.
Either way, Android doesn't come with a complete user manual, so we've compiled some of the mistakes you shouldn't make on an Android phone. They include ignoring security features and trying advanced functions without understanding them. Follow these, and your Android phone should last years in good condition.
1. Skip software updates
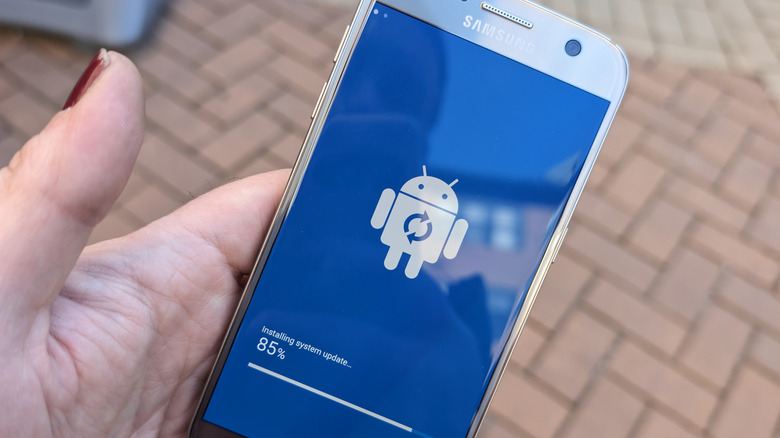
Why it's bad: Software updates fix known vulnerabilities. Patches in a software update are often responsive, meaning they protect against attacks that are happening, not just theoretical threats. Also, if you use high-security apps like banking and wallet tools, those services won't work if your phone gets too behind on security updates.
Who says so: Security vulnerabilities in Android are reported to Google, and Google shares this information confidentially with Android device makers. You can read about what threats Google considers critical on its Android Security page.
Google doesn't share this information publicly for 90 days, giving vendors time to create proper patches and preventing would-be attackers from taking advantage of the details before people have a chance to install patches. There are a lot of players here: Google is responsible for Android software, then every phone maker adds software to Android devices that needs to be patched. Chip makers like MediaTek and Qualcomm also need to patch the drivers that allow those chips to function properly.
What's the best practice: Install every security update as soon as it appears. Also, open the Google Play Store and make sure to update apps regularly — automatic updates are best.
2. Neglect basic Android maintenance
Why it's bad: When your phone is running too many processes at once, it slows down. That seems obvious, but what's actually happening is your phone is shuttling apps between three internal components: storage, RAM and a special partition of RAM called ZRAM made to quickly store and recall active processes.
When your RAM fills up, it starts compressing processes so it can cram them into the ZRAM partition. When there's no more room in ZRAM for compressed data, your phone enters a state called memory thrashing, where it repeatedly loads data from the ZRAM and then compresses it back in an ongoing cycle. This causes your phone to slow down and heat up as the CPU drains power.
Who says so: The Android Open Source Project offers technical details on the so-called "low memory killer daemon" (the software process that stuffs data into ZRAM), and the problems caused when you let that memory fill up with extraneous data pages.
What's the best practice: Restart your phone regularly to clear the RAM and ZRAM. When you're done with a heavy app like a game, swipe to close it from the app switcher menu (though you don't need to do this constantly for all apps). Finally, uninstall apps that you no longer use to make sure they aren't running processes you don't need. On Android, even if you don't open an app, it may still run and use your RAM in the background.
As another part of core maintenance, make sure to keep enough space free on your Android phone. Running it with maxed-out storage means it has no room for temporary caches and other "helper" data.
3. Install apps from untrustworthy sources
Why it's bad: There is no easier way for bad actors to take advantage of security flaws than from apps that come from outside Google's Play Store garden. One common practice is for bad apps to take advantage of your phone's Accessibility controls, which grant privileges for copying your phone's screen and running apps in the background. Google is cautious about approving accessibility access on the Play Store, which is why bad apps are often found on third-party sites.
Who says so: According to Google's security blog, Google Play Protect identified more than 13 million malicious apps from outside the Play Store in 2024 — and those are just the ones the service was able to detect. The standards for Android app security are set by the App Defense Alliance, part of Linux, which forms the foundation of Android's code.
What's the best practice: If you must install apps from outside Google Play, make sure you 100 percent trust the source. A first-party developer you trust, or a security-conscious third-party app market like F-Droid, is better than a random forum or Reddit page. Always use caution outside the Google Play Store.
4. Disable Android's security protections
Why it's bad: If you're asked to disable Google Play Protect for any reason, that's a major red flag. Usually, a scammer will try to convince you to download a phony app by pretending to be your bank or another trusted source. When you try to install the new app, you get a warning from Play Protect, which the scammer tells you to disregard. Never ignore this warning.
Who says so: Play Protect has been a part of Android for almost 10 years, and it gets constant updates that make it more stringent. It's the primary line of defense against dangerous apps you try to install.
What's the best practice: Never disable Google Play Protect, but don't trust it blindly either. Researchers like Bitdefender claim to have found apps that made it to the Play Store and still pose a risk, so you still need to be careful about what you install.
5. Root your phone without a good reason
Why it's bad: In the early days of Android, there were good reasons to obtain root access to your phone. You could enable features that were inexplicably turned off, like network tethering on Verizon's early Android devices. It allows you to remove bloatware installed by your mobile carrier, or even load an OS like CyanogenMod that was better than what Samsung or Google provided. Those days are over.
Rooting a phone triggers failures in Google's Play Integrity API, and that's a break that can't heal. You won't be able to use banking or financial apps or any apps that rely on your phone's integrity, a tag that disappears when you obtain root access to your system. Having root access means mistakes or malicious apps can cause much more damage.
Who says so: Even the US government says this is a bad idea. The National Institute of Standards and Technology (NIST) warns against rooting your mobile device, listing rooting and jailbreaking a phone as a threat in its Mobile Threat Catalogue.
What's the best practice: There is not enough reason to root your primary Android phone today if you aren't a software developer. Phone features are no longer restricted based on which carrier sold you the phone. And phone makers let you remove (or at least hide) the bloat — you can even remove Google apps that used to be permanently stuck in your app drawer.
If you have an old device that no longer gets updates, rooting and installing a custom ROM can bring new life to it, but the trade-offs aren't worth it on an in-support daily phone.
6. Use advanced tools that you don't understand
Why it's bad: Say your new Android phone came with a bunch of apps you don't want. The Settings menu lets you disable them so they disappear, but they're still taking up space and you can't let it go.
So, you found a YouTube video that shows you how to turn on USB Debugging, which lets you manage your phone's files from your PC. You figure this isn't a problem, since you aren't installing anything from a third party or handing your phone to a stranger.
Except those instructions often skip an important final step: remember to turn USB Debugging off. Otherwise, your phone is more vulnerable to attacks using a computer. While Android requires you to authorize the connection when you connect to any PC for the first time, you might not realize what you're doing, or someone could trick you into handing over access. That's why it's important to watch the prompts when connecting to an unknown USB port (more on this below).
There are lots of features on Android that can give you advanced access to your system without being dangerous, as long as you're careful to turn them off when you're done.
Who says so: Google is enthusiastic about Android users trying Developer Mode, but admits "it's essential to understand the implications of each setting." That's a massive understatement, since these options can cause problems if you don't know what they do.
What's the best practice: If you dabble in the Android cauldron, be sure to put out the fire. Disable USB Debugging and any other features that you turned on once the task is done. Follow instructions closely, and don't mess with features you don't truly understand.
7. Use public Wi-Fi for sensitive matters
Why it's bad: When you access an open Wi-Fi network, you have no guarantees of privacy. Anyone else who joins the network can use free analyzer tools to see what's happening. Almost every modern website uses HTTPS, meaning information you send to a site (like login credentials) is encrypted. But someone snooping on the network would still be able to see which sites you're accessing.
Even if the network seems trustworthy, it's hard to be sure. For example, say you use the password on the wall to connect to a cafe network. Someone could have set up a fake network with the same name and password combination, and your device won't know the difference. It looks for the strongest connection, which might be the person next to you with a sketchy hotspot and Wi-Fi sniffer, not the router mounted above the ceiling.
Who says so: The US Government's Cybersecurity and Infrastructure Security Agency said public Wi-Fi networks are one of the biggest threats for high-risk security attacks, though this was in 2012 before HTTPS was as common as it is now. Technology departments at universities like Vanderbilt continue to warn of the risks and how to mitigate them.
What's the best practice: Use a VPN for another layer of encryption on untrusted networks. If you must use public Wi-Fi without a VPN, avoid working with sensitive info like bank details. And if a site doesn't use HTTPS, leave it for when you're at home.
8. Plug your device into untrusted ports
Why it's bad: When you plug into a USB port, you are often connecting your phone to both a power source and a data connection. Your phone will prompt you to trust a new device for data connections, which is where the risk comes in. If you grant that access, an attacker could steal your photos, load malware onto your phone or intercept communications, among other harmful actions.
Who says so: The FCC has issued warnings against plugging your phone into unknown USB ports. While no reports of so-called "juice jacking" attacks have happened in the real world, the technique has been demonstrated multiple times at hacking events (first at the Black Hat security conference in 2013). There's even a USB cable called the O.MG sold by an InfoSec testing company, Hak5, that contains the necessary hardware to pull off a juice jacking attack — for testing purposes, of course.
What's the best practice: When you plug your phone in at an airport, don't accept any pop-up notices that appear. If possible, use a proper wall outlet or a portable charger to eliminate the small theoretical risk of these attacks.
9. Ignore app permissions
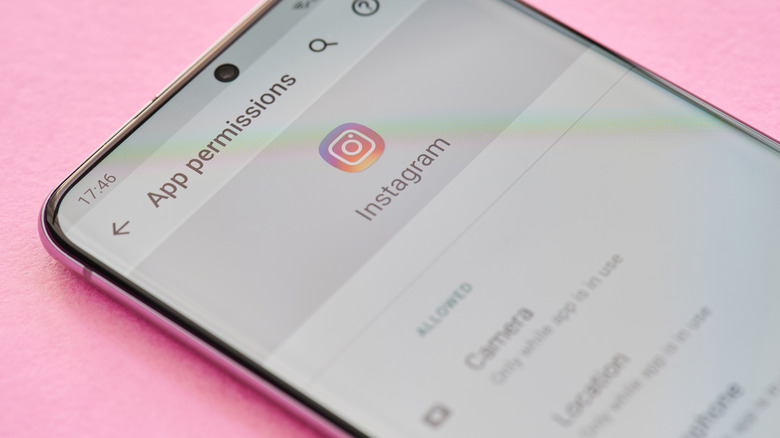
Why it's bad: Apps often ask for more information than they need. Does a calculator app need access to your photos? Does a flashlight app need to use the microphone? Those are obvious examples of permissions you should be critical of. More important are Accessibility permissions, which allow an app to monitor everything on your screen, monitor your SMS messages (for 2FA codes, for example) and even control other apps without your knowledge. That sketchy to-do list app could open your banking app, change your password and have its way with your accounts, if it has proper accessibility access.
Another permission to watch is Display over other apps. This lets Facebook float Messenger chat heads on top of your home screen and other apps, but could also let a bogus app overlay a fake button that gives permission to further abuse. It may look like you're tapping in the Google Play Store, when the button is actually a separate app that will install a nasty payload.
Who says so: Android takes permissions seriously: the latest versions of Android revoke all permissions from apps you haven't used in a long time, just to be safe. Google tells developers to ask for permissions incrementally, and only when a feature is needed, so you have context for why the app is asking.
What's the best practice: You know to be careful with microphone and camera access, but also be aware when an app asks for any unusual permissions. Regularly review your permissions and remove any that are unnecessary (or uninstall apps you never use).
10. Fail to take care of its battery
Why it's bad: Lithium batteries hate extremes. When one is always kept at 100 percent, it increases the wear on internal components and reduces the total charge the battery can hold over time, according to Samsung. That's why modern iOS and Android versions come with battery management tools that keep your phone around 80 percent while you charge overnight, only topping up to 100 percent just before you wake up.
You should also avoid using cheap, off-brand USB cables for charging. Your phone came with a high-quality USB cable that includes a controller chip to make sure the device gets a steady voltage. Cheap USB cables often lack that chip, which can cause your battery to overheat. At worst, it can cause internal electrical damage, though any excess heat is bad for your battery's chemistry. It speeds up reactions and can cause the battery to degrade faster.
Who says so: Most phone makers have a warning page about batteries, with battery utilities recommending that you only charge your phone to 80 percent under normal circumstances. This will extend the longevity of the battery, which is a good idea if you plan on keeping your phone for many years.
What's the best practice: Let Android do its job. Your phone has software that helps manage battery, both for day-to-day life and overall longevity. Don't force your phone to charge past Android's recommended limit all the time.